Memory Corruption and 6 Severe Linux Kernel Flaws: Should You Switch Your Steam Deck and SteamOS to Beta?
Coordinated vulnerability disclosure in the Linux kernel normally follows an ironclad sequence: researchers send their findings to the private security mailing list (security@kernel.org), maintainers quietly build and test a patch behind closed doors, and the technical write-up only goes public once stable updates are ready to roll out. Between October 21 and October 22, 2026, that safety net broke down completely. Six unpatched Linux kernel vulnerability reports from Trend Micro's Zero Day Initiative (ZDI) landed directly on the public Linux Kernel Mailing List (LKML) before mainline fixes were merged. With severity ratings climbing as high as 9.0 out of 10 on the CVSS scale, the sudden exposure has left many Linux gamers on SteamOS, Bazzite, and Nobara wondering whether they should move their Steam Deck and desktop rigs onto beta update branches.
Six Unpatched Flaws Posted in Public and Greg Kroah-Hartman's Swift Rebuke
As the six detailed vulnerability advisories hit the public archives on lore.kernel.org, Linux stable kernel maintainer and second-in-command Greg Kroah-Hartman stepped in within minutes. Replying individually to each submission from the Zero Day Initiative, Kroah-Hartman publicly questioned why unpatched security flaws were being broadcast to an open mailing list without accompanying fixes, urging the organization to fix its submission pipeline immediately.
A closer look at the advisory headers reveals a fascinating wrinkle behind the leak: the reports credit TrendAI, Trend Micro's automated artificial intelligence vulnerability scanner, as the discoverer. Back in May 2026 during the Linux 7.1 cycle, kernel developer Willy Tarreau rewrote the official security-bugs documentation following Linus Torvalds's complaint that duplicate AI-generated bug reports had rendered the private security list nearly unmanageable. Under the updated kernel policy, flaws uncovered by AI tools must be treated as already public and sent straight to subsystem maintainers on public lists, provided they include a patch or a rigorous impact analysis. By dispatching raw, unpatched vulnerability reports to the open list without fixes attached, ZDI inadvertently exposed critical attack vectors before official CVE identifiers could even be assigned.
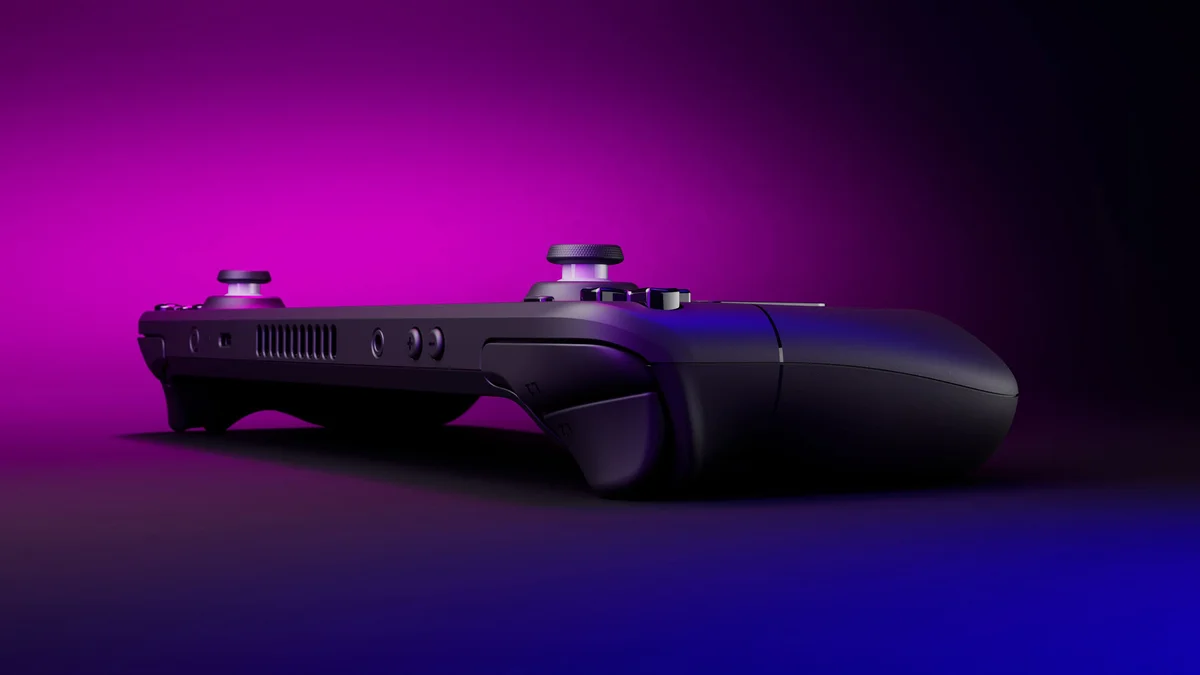
Technical Breakdown of the 6 ZDI Linux Flaws: From KSMBD to the Network Stack
Not all six vulnerabilities disclosed in this batch carry the same weight for a handheld console or a gaming desktop. Here is the exact breakdown of the tracking identifiers posted to the mailing list:
- ZDI-CAN-33549 (CVSS 9.0, Remote Code Execution): An integer underflow vulnerability in the SMB Direct (RDMA) path of KSMBD, the in-kernel SMB3 file server. When a client sends RDMA memory descriptors where the first entry exceeds the declared payload size, the internal size counter wraps around to a massive integer and triggers a buffer overflow during a subsequent memory copy. A patch was already sitting in a Git branch queued for Linux 7.5 and is now expected to be fast-tracked into mainline and stable trees.
- ZDI-CAN-33774 (CVSS 9.0, Pre-Authentication Remote Code Execution): A critical race condition in how KSMBD selects protocol handlers for incoming requests, demonstrated against Linux 7.3-rc3. By sending a burst of short SMB1 packets immediately followed by an SMB2 packet within the same TCP write over port 445, an unauthenticated remote attacker can force the SMB2 worker thread to read past the end of the smaller SMB1 buffer, leaking kernel heap memory and enabling an out-of-bounds write when parsing security descriptors.
- ZDI-CAN-33367 (CVSS 7.8, Local Privilege Escalation): A flaw in the Linux kernel networking stack's socket buffer zero-copy handling (
skbuff/skb-zerocopy). Kernel developers had independently received a report covering this exact same bug from another researcher a week earlier, and a mainline patch is expected imminently. - ZDI-CAN-34068 (CVSS 8.8, Local Privilege Escalation): An out-of-bounds write vulnerability inside vmwgfx, the virtual GPU driver used by VMware guest virtual machines on Linux.
- ZDI-CAN-34076 (CVSS 8.6, Information Disclosure): An uninitialized resource bug in the kernel's NVMe over Fabrics target (nvmet) driver that can leak sensitive memory data.
- ZDI-CAN-32005 (Local Privilege Escalation): A stack buffer overflow triggered by search-domain TCP queries inside ConnMan, a lightweight user-space network connection manager widely used across embedded Linux setups.
What It Actually Means for SteamOS, Steam Deck, and Linux Gaming Distros
With headline CVSS scores hitting 9.0 so soon after recent web infrastructure security scares that disrupted the Steam Store, should you worry about a remote attacker hijacking your Steam Deck or Bazzite PC? Regarding the two CVSS 9.0 remote code execution flaws (ZDI-CAN-33549 and ZDI-CAN-33774), there is a crucial distinction to keep in mind: KSMBD is not Samba. Originally written by Samsung as a high-speed in-kernel SMB3 server, KSMBD is disabled by default on almost all desktop Linux distributions and does not run on a stock Steam Deck unless a user has manually configured kernel-level SMB file sharing over port 445. Home NAS appliances and dedicated servers running ksmbd-tools on untrusted networks are the real targets here.
However, the local privilege escalation flaw in the networking stack's skbuff zero-copy code (ZDI-CAN-33367) and the ConnMan buffer overflow (ZDI-CAN-32005) affect far more common networking components. If you frequently dock your Steam Deck in KDE Plasma Desktop Mode on public Wi-Fi networks, run third-party scripts outside Flatpak sandboxes, or share your machine with multiple local accounts, getting patched kernel builds as early as possible makes practical sense.
Check Availability for Valve Steam Deck OLED on Amazon→
How to Switch SteamOS to Beta Channels and Check Your Linux Kernel
Because several of the incoming mitigations are currently undergoing testing in linux-next and release-candidate trees before trickling down to locked stable kernels, opting into an early update branch lets you pull newer kernel builds faster, part of the ongoing Linux software pipeline that Valve is already refining ahead of next-generation AMD Zen 6 handheld hardware spotted on Linux.
To switch your Steam Deck (LCD or OLED) to a newer SteamOS branch:
- Press the physical STEAM button on your handheld to bring up the main navigation menu.
- Select Settings and scroll down to the System tab.
- Under the Beta Participation section, open the System Update Channel drop-down menu.
- Select Beta (or Preview, which tracks Valve's latest SteamOS 3.9 builds rebased onto Linux kernel 7.2 alongside newer Arch Linux packages), download the update, and restart your system.
On a traditional Linux gaming desktop or inside Konsole in SteamOS Desktop Mode, you can also verify in seconds that the KSMBD kernel module is not loaded by running lsmod | grep ksmbd. If it happens to be active on a machine that does not need kernel SMB sharing, unload it immediately with sudo modprobe -r ksmbd and ensure TCP port 445 is blocked at your firewall.
My Test Bench: Should You Actually Leave the Stable Channel on Your Steam Deck Today?
From my perspective testing Linux handhelds daily, the right move depends entirely on how you use your hardware. On my own Steam Deck OLED, when the device stays in Game Mode behind a home NAT router simply launching verified Steam titles, the two CVSS 9.0 KSMBD bugs pose virtually zero threat because that kernel SMB server module is never loaded in the first place. On the other hand, if you treat your Steam Deck as a full-fledged Linux laptop on the road, tethering to hotel Wi-Fi in Desktop Mode and running unverified community tools, the local privilege escalation bug in skbuff is a strong reason to watch the SteamOS Beta and Preview changelogs closely over the next few days. The real takeaway here is the unintended consequence of the kernel's May 2026 AI reporting rule: a policy designed to keep AI-generated spam out of the private security list just ended up putting six unpatched kernel flaws in plain sight for everyone to read.
PC hardware enthusiast and competitive gamer, Arthur 'Heimdall' splits his time between France and the UK working in enterprise B2B software solutions. A business school graduate passionate about component benchmarking, he has been building, modding, and tuning PCs since childhood, optimizing every thermal degree and millisecond of display latency. An avid gamer across Assassin's Creed and sandbox titles, he forged his alliance with Grimtag and Chaya during late-night World of Warcraft raids before joining Pro-Gamer.