First Nintendo Switch 2 ROM Dumps Surface Online: Why These Extracted Game Files Remain Completely Unplayable
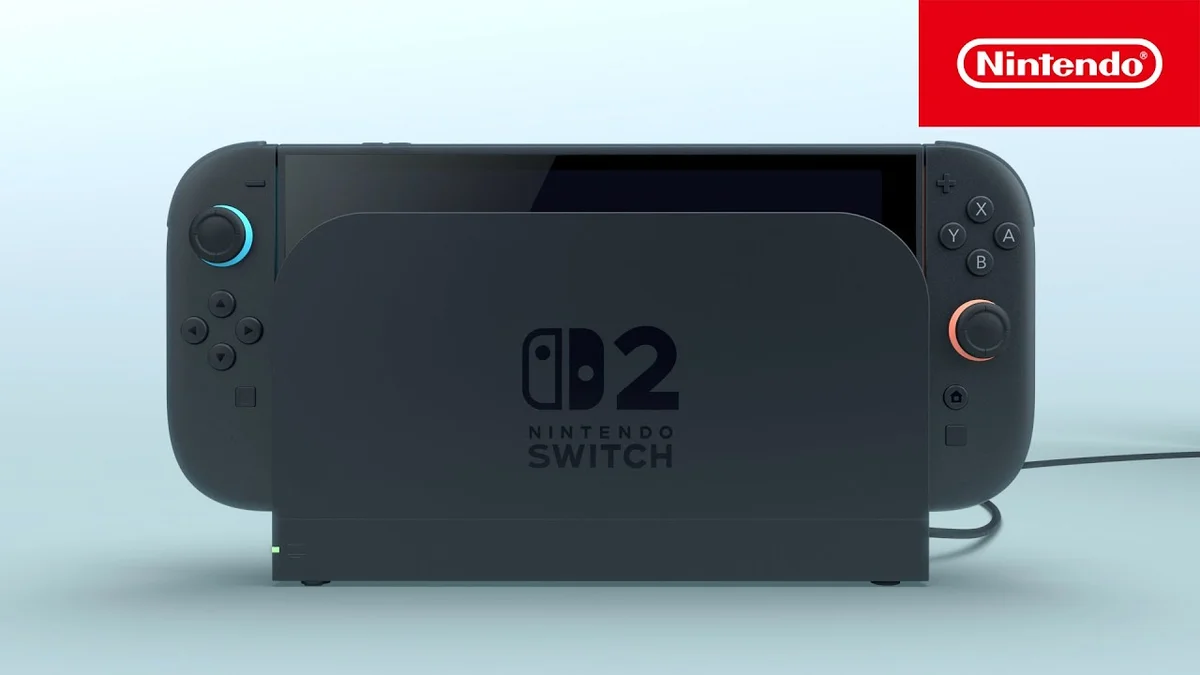
Over the past few hours, headlines claiming that the first "Nintendo Switch 2 ROMs" have leaked online have been making the rounds across social media and gaming forums. In late October 2026, extracted file directories from several official titles for Nintendo's new hybrid console did indeed begin surfacing through security researchers and archiving groups. However, beneath the sensational buzz, the technical reality tells a completely different story: these files are neither standalone encrypted cartridge images nor playable game backups, and they remain entirely unplayable.
From ns2jb to OunceCake: How Nintendo Switch 2 Game Assets Are Being Extracted
To understand what is actually circulating online, we have to look at the software-based userland exploit chain known as ns2jb, recently documented by security researcher Sammy Hajhamid (known online as pepsipu) and expanded with a Remote Procedure Call (RPC) server by developer Kurumuz. Building upon this user-space entry point, developer misshexa66 released an open-source utility called OunceCake, a nod to the Nintendo Switch 2's internal codename, "Ounce."
Unlike traditional hardware dumpers that cloned full physical cartridges into XCI or NSP container formats on the original Switch, OunceCake does not break the hardware-level encryption of Switch 2 game cards. Instead, the utility waits for the console's operating system to naturally mount and decrypt a legitimately owned game in system memory during normal execution. Once the title is running, the RPC hook exposes the decrypted RomFS (which holds 3D models, textures, scripts, and audio tracks) and ExeFS (executable binaries) partitions over a local FTP connection, allowing researchers to transfer and inspect the raw folder structure on a PC.
Through this datamining process, raw asset folders from titles such as Mario Kart World, Chapters 1 through 4 of Deltarune, and the network beta build of FromSoftware's console exclusive The Duskbloods have been extracted for technical analysis and asset preservation:
Hardware Encryption Keys, Locked Kernel, and Zero Emulators: Why These Dumps Are Unplayable
While pulling unencrypted RomFS directories is a notable milestone for dataminers studying game engines, it hits an immediate brick wall when it comes to actual execution. The foothold provided by ns2jb is strictly confined to userland privileges. The Nintendo Switch 2's hypervisor, operating system kernel, and hardware-rooted cryptographic chain of trust remain completely uncompromised.
Furthermore, the updated physical cartridge protocol and Nintendo's private master encryption keys have not been breached. Without kernel-level access or the cryptographic keys required to sign and validate packages, loose RomFS and ExeFS asset folders cannot be repacked into bootable images or launched on another console. The landscape is further complicated by Nintendo's adoption of Game-Key Cards for several physical releases, where the cartridge acts primarily as a cryptographic hardware token rather than storing the full game binary offline.
Above all, no Nintendo Switch 2 emulator exists today, not even in a preliminary state. Building a functional emulator or exploring alternative preservation methods like native static recompilation on PC requires years of clean-room reverse engineering and deep architectural documentation. At a time when the industry is ramping up enforcement against retro handhelds loaded with pirated ROMs targeted by the ESA, security researchers are also warning players to stay vigilant: shady websites currently advertising "playable Switch 2 ROMs" or miracle PC emulators are exclusively distributing dummy files, adware, and malware designed to compromise unsuspecting users.
My Perspective
It is striking how quickly the phrase "ROM dump" triggers wild misconceptions whenever a Nintendo console is involved. Looking closely at how ns2jb and OunceCake actually operate, I am mainly struck by how thoroughly Nintendo learned from the original Switch's security flaws. Back in 2017 and 2018, an unpatchable hardware bootrom vulnerability in the Tegra X1 chip handed researchers full control of the system early in its lifecycle. With the Switch 2, the hardware fortress is holding firm: inspecting 3D models or audio files from a game you already own and run legitimately in memory is datamining, not piracy or playable emulation. As long as the kernel and master encryption keys remain locked behind Nintendo's hardware security layers, these extracted folders are strictly study material for researchers, and I strongly advise players to steer clear of the fake download links already preying on the hype.
Based on the outskirts of New York City, Chaya 'Chayane' spent five years studying software engineering in Montreal before returning to her home state. A Full-Stack developer and Deep Learning AI architecture researcher, she explores neural networks and algorithmic optimization while engineering data pipelines for Retrocharting and Gamescharting alongside Grimtag. A gamer for over 20 years and an avid collector of Nintendo history and The Legend of Zelda, she explored World of Warcraft's Azeroth before bringing her deep technical background to video game analysis.