Missing 2FA and Unverified Password Changes: Why Humble Bundle's "Vibe-Coded" Redesign Has PC Players Removing Their Credit Cards
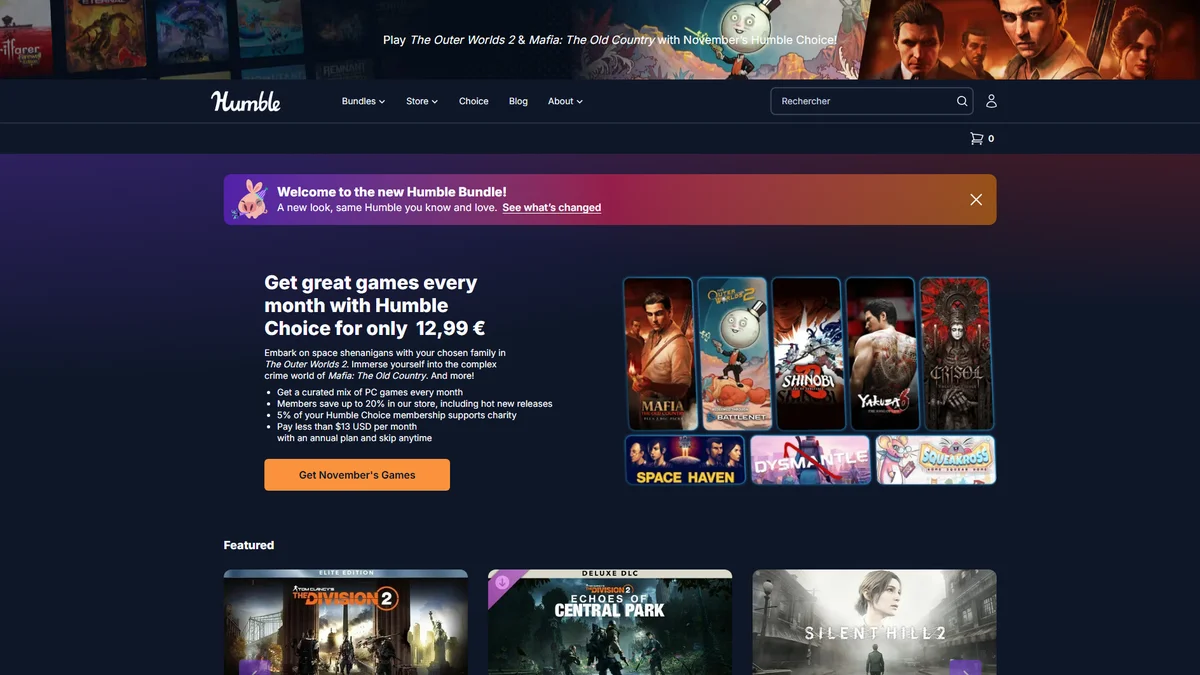
Greeted by a cheerful "Welcome to the new Humble Bundle" banner promising a fresh look for the longtime charity PC storefront, users quickly discovered a far more alarming reality upon opening their account settings on November 12, 2026. Behind an interface overhaul that developers and community members across the r/humblebundles subreddit have widely criticized as a hastily generated "vibe-coded" redesign, the update has stripped away foundational security protections for customer accounts.
TOTP Two-Factor Authentication Vanishes Alongside Password and Email Verification
The most glaring regression affects two-factor authentication (2FA). Customers who previously secured their profiles using TOTP authenticator apps found that the 2FA management section has completely vanished from Humble Bundle's security settings, and login prompts no longer ask for a verification code.
Upon inspecting the updated credential management workflow, security-minded users uncovered three critical vulnerabilities that leave accounts exposed to unauthorized takeovers:
- Password changes without current password verification: while logged into an active session, anyone with access to the browser can set a new password immediately without entering the existing password or even typing the new password twice to confirm.
- Email updates with zero alert to the original address: changing the email address tied to an account sends no confirmation link or security warning to the old email inbox. Verification messages are routed solely to the newly entered email address.
- Persistent session tokens: updating an account password fails to invalidate existing session tokens on the backend, meaning a compromised session remains active even after the legitimate owner resets their credentials.
Why Subscribers Are Rushing to Unlink Saved Credit Cards and PayPal
These security oversights arrive at a particularly sensitive time for regular buyers. Thousands of PC players keep a credit card or PayPal billing agreement saved on file for recurring monthly bundles, especially with the November 2026 Humble Choice lineup drawing heavy traffic for Mafia: The Old Country, The Outer Worlds 2, and SHINOBI: Art of Vengeance.
Without two-factor authentication or automatic session revocation, the community consensus is unequivocal: log into your Humble Bundle account settings right now and delete any saved credit cards or linked payment methods until a verified security patch is deployed. Compounding the frustration, users report that the option to stay logged in has disappeared, checkout pages are throwing internal server errors when attempting to purchase new bundles, and several support ticket links are returning 404 errors.
Broken Key Filtering and thousands of Pages Cripple Longtime Libraries
Beyond the immediate security hazards, the redesign has severely degraded day-to-day library management for veteran collectors. Users with over a decade of bundle purchases note that the revamped library no longer distinguishes between redeemed and unredeemed Steam keys. While Valve's recent major Steam client update focused on streamlining library organization for PC players, Humble Bundle's new layout removes purchase dates, hides total money-spent metrics, breaks third-party management tools like humble-cli, and displays so few items per page that large libraries now span thousands of pages.
Developers reviewing the front-end styling pointed out that the generic component layout closely mirrors stock web templates generated by large language models such as Claude or Gemini, while public counters showing total bundle units sold and live charity split breakdowns have also disappeared from bundle landing pages.
My Take
Speaking as a developer who builds web applications every day, watching a major digital storefront push a production build that changes passwords without verifying the old one or invalidating active session tokens is genuinely terrifying. I love using AI coding assistants to speed up front-end prototyping as much as anyone, but shipping a "vibe-coded" overhaul without a basic backend security audit on authentication routes is inexcusable. You cannot replace over a decade of battle-tested account logic and key management with a generic UI shell and hope nobody checks the settings page.
Grimtag's PC Storefront Warning: If you subscribe to Humble Choice or have years of unclaimed keys sitting in your library, do not wait for an official statement: remove your saved credit card and unlink PayPal from your account today. Until TOTP two-factor authentication and original-email verification are fully restored, leaving active payment details on file is an unnecessary risk no PC player should take.
SEO consultant for over 20 years and digital entrepreneur, Charles "Grimtag" is the founder of Pro-Gamer.gg, Retrocharting.com, and Gamescharting.com. A competitive gamer, streamer, and retro game collector, he has worked in the video game industry for over 15 years, notably as a consultant for leading game price comparison platforms. Passionate about real-time performance data and gaming technology, he analyzes competitive esports, gaming hardware benchmarks, and creator workflows on Pro-Gamer.gg with an authentic player perspective.