CivSwitch Exploit on Nintendo Switch 2: How the Switch 1 Edition of Civilization VII Opens a Breach on Firmware 23.0.1
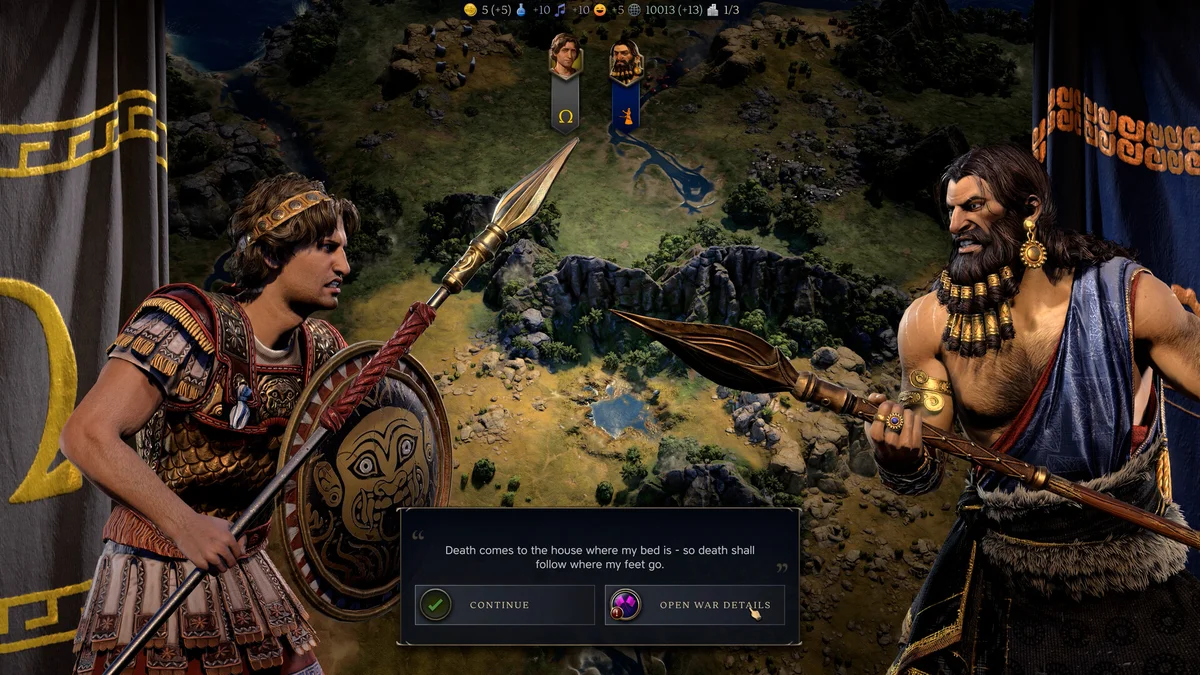
The homebrew and security research community has uncovered a clever new Trojan horse to slip custom code onto Kyoto's latest hybrid hardware. Released as an open-source project on GitHub by security researcher and developer Gezine, a new toolchain named CivSwitch establishes an offline userland entry point on both the original Switch and the Nintendo Switch 2 by leveraging the backward-compatible Nintendo Switch 1 edition of Sid Meier's Civilization VII.
Ever since Nintendo scrubbed the eShop of older digital entry vectors such as SmileBASIC, researchers have been hunting for a physical cartridge exploit that cannot be remotely revoked from the store. Following the waves caused by the ns2jb software exploit on Nintendo Switch 2 firmware 23.0.1, the release of CivSwitch demonstrates that legacy compatibility layers remain a prime testing ground across system versions ranging from 20.x.x all the way up to the current 23.0.1 firmware.
An XSS Vulnerability Hidden Inside the Version 1.0.0 Multiplayer Lobby Chat
At its technical core, CivSwitch capitalizes on a Cross-Site Scripting (XSS) vulnerability buried inside the local wireless multiplayer lobby chat of Sid Meier's Civilization VII. Because the text chat interface fails to properly sanitize specific HTML-style image error handlers, injecting a crafted string into the lobby box forces the game's UI engine to execute arbitrary JavaScript code.
Not every copy of the strategy title from Firaxis Games and 2K is eligible, however. The exploit strictly requires the unpatched version 1.0.0 physical Nintendo Switch 1 cartridge straight out of the box. Digital eShop downloads, code-in-a-box retail packages, or cartridges that have already downloaded title updates will not work. To keep the launch build intact on a Nintendo Switch 2 (where Gezine confirmed compatibility on firmwares 20.4.0 and 23.0.1, alongside 22.5.0 on original Switch hardware), users must block Nintendo's update servers beforehand using a DNS sinkhole such as 90DNS.
PicoSwitch and Persistent Save Triggers: Automating the 87-Line Injection
Because typing out a complex script manually with a controller would be nearly impossible, Gezine's toolchain splits the process into two automated components, building upon earlier JavaScript injection research from Netflix-N-Hack (and ufm42's fork) alongside Element2424's Pico-Switch-Controller firmware:
- The PicoSwitch Hardware Macro: Compiled as a UF2 firmware image for inexpensive Raspberry Pi Pico microcontrollers (supporting both RP2040 and RP2350 chips), the board emulates a USB HID keyboard when plugged into the console's dock. Once the user sets the system keyboard to US English and opens the local wireless lobby chat (Multiplayer > Wireless > Create Game > Host Lobby > Chat), the Pico automatically types roughly 87 lines of compressed code (processed via terser, deflateRaw, and base-25 chunked
img/onerrortags with profanity-filter armor) over the course of about 15 minutes. - The Remote JS Loader on TCP Port 9026: As soon as the automated typing finishes, the bootstrap payload opens a local network listener on TCP port 9026. From a PC on the same network, developers can run the companion
send_js.pyscript to push custom JavaScript files directly to the console and stream execution logs back in real time. - Persistent Save-Data Installer: To avoid waiting 15 minutes with a microcontroller on every boot, the
installer-creatormodule (`install.py`) splices the compressed payload into a modified save file (XSTRIG.Civ7Save) and writes it to the game's single-player save directory. On every subsequent launch, simply selecting "Load Game" from the main menu immediately fires up the TCP loader on port 9026, which even survives console sleep and wake cycles.
Gezine also documented a clever workaround for Japanese-region Nintendo Switch 2 units that restrict system language settings: if the console refuses direct English USB keyboard input, users can connect a secondary Switch to the same local wireless lobby and plug the Raspberry Pi Pico into the second console to transmit the chat XSS payload across the local wireless session.
What CivSwitch Actually Unlocks (And Why the Switch 2 Kernel Remains Intact)
While achieving code execution on the latest 23.0.1 firmware is a milestone for the scene, it is important to separate a userland entry point from a full system compromise. CivSwitch operates strictly within userland, meaning any executed code remains confined to the sandboxed permissions of the Switch 1 backward-compatibility container.
Out of the box, the toolchain does not provide kernel privilege escalation or full filesystem (FS) access. Consequently, it cannot install custom firmware (CFW), modify the native Switch 2 operating system, or dump native Switch 2 cartridges to feed the first public Nintendo Switch 2 PC emulators like Eden-NX2 and Eglantine. Instead, it gives homebrew developers and security researchers a reliable, eShop-independent foothold to run userland scripts and probe how the console handles legacy software containers.
My Perspective
It is one of the oldest traditions in console security: you reinforce the front door with brand-new silicon and modern cryptographic checks, only for someone to climb in through a basement window left cracked open by backward compatibility. Watching a Raspberry Pi Pico patiently type 87 lines of obfuscated code into the multiplayer chat box of Civilization VII for fifteen minutes just to turn a save file into a permanent boot trigger feels like a nostalgic throwback to the Cubic Ninja era on the 3DS or the virtual Wii mode exploits on the Wii U.
Of course, everyday players have no reason to rush out and hunt down launch cartridges right now, since everything stays locked inside a Switch 1 userland sandbox with zero access to the Switch 2 kernel. Still, Gezine's release is a sharp reminder of the cat-and-mouse game Nintendo's engineers face: once a version 1.0.0 physical cartridge ships to retail shelves with an unpatched input flaw, no amount of eShop delisting can ever erase it.
Based on the outskirts of New York City, Chaya 'Chayane' spent five years studying software engineering in Montreal before returning to her home state. A Full-Stack developer and Deep Learning AI architecture researcher, she explores neural networks and algorithmic optimization while engineering data pipelines for Retrocharting and Gamescharting alongside Grimtag. A gamer for over 20 years and an avid collector of Nintendo history and The Legend of Zelda, she explored World of Warcraft's Azeroth before bringing her deep technical background to video game analysis.